Can A Deauther Attack Be Traced And How To Protect Yourself
A deauther attack can indeed be traced through network logs, packet analysis tools, and monitoring systems. This guide covers how these attacks work, whether they leave a trace, and the practical steps you can take to protect your wireless network. Understanding Wi-Fi security threats is the first step toward keeping your devices safe.
Have you ever wondered what happens when your Wi-Fi connection drops unexpectedly? Sometimes it is just a glitch. But other times, it could be something more sinister. A deauther attack is a real threat that can kick devices off a wireless network without warning. Many people ask one critical question: can a deauther attack be traced? The short answer is yes. But the full answer is much more interesting and important.
In this guide, we will walk through everything you need to know about Wi-Fi deauthentication attacks. We will explain how they work, whether they leave a trace, and most importantly, how you can protect yourself. Whether you are a casual home user or someone who cares deeply about wireless security, this article has something valuable for you. Let us dive in.
Key Takeaways
- Deauther attacks are traceable: Network administrators and security tools can detect and log these malicious packets.
- Deauthentication frames exploit a protocol flaw: The 802.11 standard allows unauthenticated deauth frames, making this attack possible.
- Basic Wi-Fi encryption helps but is not enough: WPA2 and WPA3 reduce risk but do not fully prevent deauther attacks.
- Detection tools exist: Software like Wireshark and Airodump-ng can identify suspicious deauth traffic on your network.
- Physical tracing is possible: Signal strength, MAC address tracking, and directional antennas can help locate the attacker.
- Strong protection measures work: Using WPA3, enabling management frame protection, and monitoring your network significantly reduce risk.
📑 Table of Contents
- What Is a Deauther Attack?
- Can a Deauther Attack Be Traced?
- How to Detect a Deauther Attack on Your Network
- How to Protect Yourself From Deauther Attacks
- Can Law Enforcement Trace and Act on Deauther Attacks?
- Comparison: Deauther Attack vs Other Wi-Fi Attacks
- Common Mistakes People Make That Leave Them Vulnerable
- Quick Tips for Everyday Wi-Fi Safety
- Conclusion
What Is a Deauther Attack?
A deauther attack is a type of wireless denial-of-service attack. It targets the communication between your device and the access point you are connected to. The attacker sends fake disconnection messages, known as deauthentication frames, to force your device offline. These frames trick your device into thinking the network has gone away.
The attack exploits a weakness in the 802.11 Wi-Fi protocol. This protocol was designed long before modern security concerns became a priority. It allows any device on the network to send deauth frames without needing a password or authentication. This means even a basic Raspberry Pi running free software can launch such an attack.
How Does It Actually Work?
The attacker uses a tool to flood the network with deauth packets. These packets are sent to your device or directly to the router. Your device receives them and disconnects from the network. The attacker can target a single device or broadcast the attack to everyone in range. This makes Wi-Fi jamming a related concern, though the two are technically different.
Here is what happens step by step:
- The attacker sets up a device capable of sending raw Wi-Fi packets.
- The software generates deauthentication frames with fake source addresses.
- These frames are broadcast over the Wi-Fi channel.
- Your device receives the frames and disconnects from the network.
- The attack repeats continuously, keeping you offline.
The process is surprisingly simple. This is exactly why wireless vulnerability researchers have raised alarms for years. A deauther attack does not crack your password. It simply overwhelms the connection with forged packets.
Can a Deauther Attack Be Traced?
This is the big question, and the answer is a definitive yes. A deauther attack can be traced, but the difficulty depends on several factors. Let us break down exactly how tracing works and what makes it possible or challenging.
How Network Logs Reveal the Attack
Every access point keeps logs of network activity. When a flood of deauth frames hits the router, the logs show it. Most modern routers record the source MAC address of incoming frames. Even if the attacker spoofs their address, the router still logs the event. A network administrator can review these logs and identify the attack pattern.
Additionally, the sheer volume of deauth packets is a red flag. Normal network traffic does not produce hundreds of disconnection messages in seconds. When logs show a spike, it is a clear sign of foul play. This makes network monitoring an essential defense layer.
Tools Used for Tracing
Several tools can help trace a deauther attack:
- Wireshark: A popular packet analyzer that captures and displays Wi-Fi traffic in real time.
- Airodump-ng: Part of the Aircrack-ng suite, this tool monitors wireless networks and detects suspicious deauth traffic.
- Kismet: A wireless network detector and intrusion detection system that can flag anomalous packet behavior.
- Wi-Fi Analyzer apps: Mobile tools that show network activity and signal anomalies on your device.
These tools make it possible to not only detect the attack but also gather evidence. The captured packets can be analyzed to identify the attacker’s MAC address, signal strength, and even their approximate physical location.
Challenges in Tracing a Deauther Attack
While tracing is possible, it is not always easy. Attackers often use MAC address spoofing to hide their identity. They may also move around while launching the attack, making it harder to pin down their location. In crowded areas like cafes or airports, identifying one bad actor among many Wi-Fi devices is a real challenge.
Another difficulty is that some attacks use broadcast deauth frames. These frames do not have a single source address, making tracing more complex. However, even in these cases, directional antennas and signal triangulation can help narrow down the source.
How to Detect a Deauther Attack on Your Network
Detection is the first line of defense. If you know what to look for, you can catch a deauther attack early and take action. Here are the most common signs that your network is under attack.
Signs Your Network Is Under Attack
Watch for these warning signs:
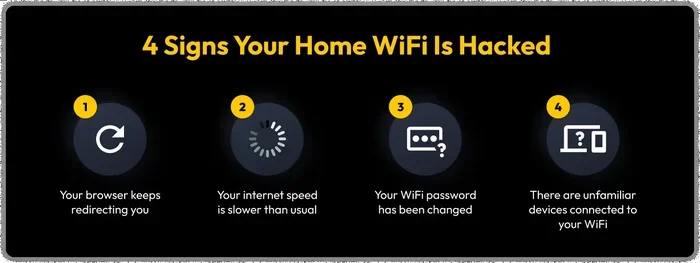
- Devices disconnecting frequently without any obvious reason.
- Multiple devices going offline at the same time.
- Your router logs show a spike in deauth frame activity.
- Your Wi-Fi connection keeps dropping even though the signal is strong.
- Other users on the same network report similar issues.
If you notice any of these signs, it is time to investigate. Use a packet sniffer or check your router’s admin panel for unusual traffic patterns.
Setting Up Detection Tools
You do not need to be a tech expert to monitor your network. Many tools are user-friendly and free. Install Wireshark on a computer connected to your network and start capturing packets. Look for a high volume of deauth or disassociation frames. If you see them, your network may be under a wireless denial-of-service attack.
For a simpler approach, many modern routers now include built-in intrusion detection features. Check your router’s settings for options like wireless intrusion detection or rogue AP detection. These features can alert you to suspicious activity automatically.
How to Protect Yourself From Deauther Attacks
Protection is always better than cure. Once you understand how deauther attacks work and how they can be traced, the next step is to make your network harder to attack. Here are the most effective strategies.
Use WPA3 Encryption
WPA3 is the latest Wi-Fi security standard. It includes features specifically designed to counter management frame attacks. One of its key protections is Protected Management Frames (PMF). When PMF is enabled, your device will reject unauthenticated deauth frames. This makes it much harder for an attacker to kick you offline.
If your router and devices support WPA3, enable it right away. Even if you must use WPA2, make sure PMF is turned on. This setting is available in most modern router configurations.
Enable Management Frame Protection
Management Frame Protection (MFP) is a must-have feature. It adds a layer of verification to management frames like deauth and disassociation frames. Without MFP, any device can send these frames. With MFP enabled, only authenticated devices can send valid management frames.
Here is how to check if MFP is active:
- Log into your router’s admin panel.
- Navigate to the wireless security settings.
- Look for an option labeled “Management Frame Protection” or “PMF.”
- Set it to “Required” or “Enabled.”
- Save your settings and reconnect your devices.
Quick tip: Not all older devices support MFP. If a device cannot connect after enabling PMF, you may need to set it to “Optional” instead of “Required.”
Keep Your Router Firmware Updated
Router manufacturers regularly release firmware updates that patch known wireless vulnerabilities. An outdated router is an easy target. Make it a habit to check for updates at least once a month. Many modern routers now offer automatic updates, so turn that feature on if available.
Monitor Your Network Regularly
Regular monitoring is one of the best habits you can build. Use a network monitoring tool to keep an eye on unusual activity. Set up alerts for high deauth frame counts or unexpected disconnections. The sooner you spot an attack, the faster you can respond.
Quick tips for effective monitoring:
- Check your router logs weekly.
- Use a dedicated monitoring device or app on your phone.
- Set up alerts for unknown devices connecting to your network.
- Review connected device lists regularly.
Physical Security Matters Too
Do not overlook physical security. A rogue device placed near your home or office can launch a deauther attack from just a few feet away. Keep your router in a secure location. If possible, place it in the center of your building to limit the signal range outside your property.
You can also reduce your Wi-Fi signal strength in the router settings. A weaker signal means a smaller attack window. This is not a complete defense, but it adds another layer of protection.
Can Law Enforcement Trace and Act on Deauther Attacks?
Yes, law enforcement agencies have the tools and authority to trace deauther attacks. Because these attacks involve unauthorized access to wireless networks, they fall under computer crime laws in most countries. When a network administrator or internet service provider detects an attack, they can share logs and evidence with authorities.
In practice, tracing a deauther attack for legal action requires cooperation between the victim, their ISP, and law enforcement. The process can take time, and the attacker must be within range of the victim’s network for tracing to work. However, the technical capability to trace these attacks exists and is increasingly being used in cybercrime investigations.
Expert insight: Many people underestimate how serious deauther attacks are. They are not just annoying. In some cases, they are used as a distraction while another attack is carried out. For example, an attacker might disconnect you from your network and then attempt to access your devices while they are unencrypted. Always take unexpected disconnections seriously.
Comparison: Deauther Attack vs Other Wi-Fi Attacks
| Attack Type | What It Does | Can It Be Traced? | How Hard to Execute? |
|---|---|---|---|
| Deauther Attack | Disconnects devices from Wi-Fi using forged frames | Yes, through packet analysis and logs | Easy with basic hardware |
| Evil Twin Attack | Creates a fake Wi-Fi network to steal data | Yes, through signal analysis and monitoring | Moderate |
| Man-in-the-Middle | Intercepts communication between two parties | Yes, with advanced network monitoring | Moderate to Hard |
| Wi-Fi Jamming | Overwhelms the Wi-Fi signal with noise | Difficult, often requires spectrum analysis | Easy but illegal |
| Password Cracking | Guesses or brute-forces Wi-Fi passwords | Yes, through login attempt logs | Moderate |
As you can see, the deauther attack is one of the easier attacks to execute. However, it is also one of the easier attacks to trace. This makes it a less attractive option for serious attackers, but it remains a common tool for pranks, disruption, and sometimes as a stepping stone for more complex attacks.
Common Mistakes People Make That Leave Them Vulnerable
Many people make simple mistakes that make them easy targets for a deauther attack. Here are the most common ones:
- Leaving their router on default settings: Default configurations often lack advanced security features like PMF.
- Using outdated WEP or WPA encryption: These older standards have known flaws and should never be used.
- Ignoring router firmware updates: Outdated firmware leaves your router exposed to known exploits.
- Not monitoring connected devices: If you do not check who is on your network, you will not notice suspicious activity.
- Using weak Wi-Fi passwords: A weak password makes it easier for attackers to gain deeper access after a deauther attack creates a window of opportunity.
Avoiding these mistakes alone will not make you invincible, but it dramatically reduces your risk. Think of each step as adding a lock to your front door. The more locks you have, the harder it is for someone to get in.
Quick Tips for Everyday Wi-Fi Safety
Here are some quick, practical tips you can apply today:
- Turn on WPA3 or WPA2 with PMF on your router.
- Change your default router admin password immediately.
- Use a strong, unique Wi-Fi password with at least 16 characters.
- Disable WPS (Wi-Fi Protected Setup) as it can be exploited.
- Create a guest network for visitors to keep your main network isolated.
- Turn off your Wi-Fi when you are not using it, especially in public spaces.
- Use a VPN on public Wi-Fi to add an extra layer of encryption.
- Regularly review your router’s connected device list.
These tips take just a few minutes to set up but offer significant protection. A few small changes can make a big difference in your wireless security posture.
Conclusion
The answer to the question “can a deauther attack be traced” is a clear and reassuring yes. These attacks leave traces in network logs, packet captures, and router records. With the right tools and knowledge, both individuals and professionals can detect, trace, and even locate the source of a deauther attack. The fact that tracing is possible serves as both a deterrent and a tool for accountability.
But tracing is only half the story. The better approach is prevention. By enabling management frame protection, using strong encryption like WPA3, monitoring your network, and following the practical tips in this guide, you can significantly reduce your risk. A deauther attack does not have to be something you fear. With the right knowledge and tools, you can stay connected safely and securely.
Take action today. Check your router settings, update your firmware, and start monitoring your network. Your wireless security is worth the effort.
Frequently Asked Questions
What exactly is a deauther attack?
A deauther attack is a type of wireless attack where an attacker sends fake disconnection messages to kick devices off a Wi-Fi network. It exploits a flaw in the 802.11 protocol that allows deauthentication frames to be sent without needing a password. The attack does not crack your Wi-Fi password but simply disconnects you from the network.
Is a deauther attack illegal?
In most countries, launching a deauther attack without authorization is illegal. It falls under computer crime and wireless interference laws. Even if the attack does not steal data, it disrupts network services and can be prosecuted. Always use security tools and knowledge responsibly and ethically.
Can a deauther attack steal my personal data?
A deauther attack itself does not steal data. However, it can be used as part of a larger attack strategy. For example, an attacker might disconnect you from your secure network and then attempt to intercept your traffic when your device reconnects to an open or less secure network. This is why staying vigilant and using a VPN is important.
What devices are vulnerable to deauther attacks?
Any device that connects to Wi-Fi can be affected. This includes smartphones, laptops, smart home devices, tablets, and even IoT gadgets. The vulnerability lies in the Wi-Fi protocol itself, not in any specific device. However, devices that support WPA3 and management frame protection are much harder to attack.
How can I tell if my network has been targeted by a deauther?
Look for sudden, repeated disconnections across multiple devices. Check your router logs for spikes in deauthentication frames. Use tools like Wireshark or Wi-Fi analyzer apps to monitor for unusual traffic patterns. If several devices go offline at the same time without a clear reason, a deauther attack may be the cause.
What is the best defense against deauther attacks?
The best defense is a combination of WPA3 encryption, management frame protection (PMF), regular firmware updates, and active network monitoring. These measures make it significantly harder for attackers to succeed and help you detect and respond quickly if an attack occurs. No single step is foolproof, but together they create a strong defense.
=== CONCLUSION ===
Can a deauther attack be traced? Absolutely. And now you know exactly how and why. The key is to stay informed, stay proactive, and take the protection steps outlined in this article. Wireless security is not something you set and forget. It requires regular attention and smart habits. Start with the basics, build from there, and enjoy peace of mind knowing your network is well-protected.